

Let's Go
Phishing
phishing - /ˈfiSHiNG/
The fraudulent practice of sending emails or other messages purporting to be from reputable companies in order to induce individuals to reveal personal information, such as passwords and credit card numbers
- Oxford Dictionary
Security experts agree that phishing is one of the leading security risks faced by businesses and individuals. Phishing is a criminal act where the victim is contacted via phone, text, or email and is intentionally deceived by the perpetrator in order to gain personal information. It is classified as a “social engineering” attack as it uses the victims’ trust in institutions such as government, banking, healthcare, etc. Phishing attacks can range from the easy to spot fakes to elaborately constructed emails and websites.
The ink had barely dried on my previous blog post on improving email security when a reasonably well-constructed phishing attack bypassed the spam filters and hit my inbox. This gave me the idea to expand on the previous blog post with a deeper dive into this form of cyber attack.
Can You Spot the Fake?
This is not a trick question. One of these screenshots is indeed genuine.


At first glance it can be really hard to discover the fraud
Let’s compare the two emails more closely and develop some skills to more quickly identify any fraudulent emails that might escape detection by your spam filter.
- Corporate Logo
- Expected Corporate Colors
- Expected Corporate Branding
- Identifies Me By Name
- Tracking Number
- Shipper Information
- Delivery Time Information
- Mobile App Download Button
- Copyright Statement
- Additional Website Links
- Corporate Logo
- Expected Corporate Colors
- Expected Corporate Branding
- Identifies Me By Name
- Tracking Number
- Shipper Information
- Delivery Time Information
- Mobile App Download Button
- Copyright Statement
- Additional Website Links
The fact that both emails convey similar information makes the fraudulent one much more difficult to spot.
Spot It Yet?
- FRAUD
- REAL
Social Engineering
Scammers use misdirection and manipulation in the following way
They Present Something Familiar
To Establish Trust
To Encourage Action
The fraudulent shipping notification above is a masterclass on presenting familiar imagery to establish credibility and gain trust and encourage the receiver of the email to act. What specifically do they want? They want you to click any of the embedded links in the email and once that has been done they have you and can phish for information.
They only need to keep you convinced for a few seconds to get what they want
If we examine the email more closely the fraud becomes obvious very quickly. Here are some of the techniques that this scammer used to build this email and where it falls apart.
Corporate Branding
In order for the fraud to be believable the scammer used the “look and feel” of legitimate emails. This means replicating the logos, colors, style, fonts, page layout, and phrasing. The scammer does an excellent job of getting the details correct in the impersonation.
- Corporate brand and background color values match
- Corporate logos match
- Embedded link colors match
- Mobile App download link match
Here is where things fall apart
- The mail looks a bit too pretty for a simple notification –
- The overuse of photos and other visual elements is part of the deception
- The use of visual information to mask details
- The use of graphics with links provides lots of items to click on
- The copyright year isn’t correct 2018 versus 2023
- The information conveyed is vague and noncommittal
- The details provided don’t hold up to scrutiny

Web Links
The entire purpose of a fake email is to redirect you to a space that the scammer controls and then convince you to voluntarily give some pieces of personal information. The sample fake email accomplishes this by including a dozen web links all directing you to the same location.
Legitimate emails from institutions that contain multiple links will all direct you to different places on their website. It is highly unlikely that any two links in a legitimate email lead to the same place.
What's Wrong Here

All the phishing links highlighted
- Nearly a dozen links in email
- All links lead to the same location
- Styled to encourage clicking
- Links do not direct to intended website
- Uses visual clutter to hide detail
- Information looks credible at a glance
- Only detail given is the tracking number
- Most information is general

How to Undercover a Fake
Be Suspicious of Unexpected Email Notifications
Be suspicious of emails unexpected emails from popular institutions that tend to send a lot of emails. This can be really challenging as most of us order lots of goods and services online. My previous blog on email security goes into detail about using multiple email accounts for specific types of interactions. This makes unexpected emails easier to spot and never open in the first place.
Use the Preview Feature if Your Email Client Has One
Use caution when opening emails from the following sources. Avoid clicking links embedded in an email and NEVER open any attached documents or files
- Retailers – online shopping can result in lots of advertising emails. Verify that they are genuine and consider un-subscribing. Better yet, opting out of most email interactions when making purchases
- Shopping Sites (Amazon, eBay) – scammers often try to mask as Amazon or eBay. Verify that the email sources are genuine.
- Social Media – scammers also imitate popular social media platforms as we are conditioned by them to expect regular email notifications. Turn off as many email or text notifications as possible.
Don't Trust Spam Filters To Catch Everything
NEVER OPEN emails if the following is true. NEVER click any embedded links in questionable emails, and NEVER open any attached documents or files
- Missing Subject Lines – Emails missing a subject line are usually caught by spam filters but some can make it through
- Garbled or Nonsense in the Subject Line – If the subject is not clearly readable in English or any other languages that you commonly speak
- Spelling or Grammar Errors in the Subject Line – Spammers and scammers oftentimes aren’t native speakers and make obviously sometimes comical mistakes. Filters usually catch these but not always
Take Notice of Who Sends You Emails
A lot can be revealed by the email address of the Sender. Legitimate emails will always come from the registered domain or sub-domain of the institution. At a quick glance, it may be difficult to spot the imposter.
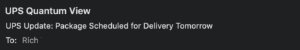
- FRAUD
- "noreply@ups1.com" is a fraud
- Track Number missing in Subject Line
- Details are vague or non-specific
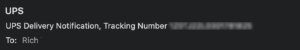
- REAL
- "noreply@ups.com" is a genuine
- Tracking Number in Subject Line
- Details provided are specific
How to Verify a Domain
Domain owners of legitimate businesses want you to know who they are online. They go to great lengths to ensure that their domain registration information is updated and contains valid contact information. Anyone can obtain information about a web domain free of charge. The following two websites will provide registration information for any domain.

- FRAUD
- Doesn't identify the institution by name
- Lacks contact information
- Registrar is non-US based

- REAL
- Institution is identified by name
- Full contact information provided
- Registrar is US based
Legitimate institutions want you to know who they are
WHAT IS ICANN?
The Internet Corporation for Assigned Names and Numbers (ICANN /ˈaɪkæn/ EYE-kan) is an American multistakeholder group and nonprofit organization responsible for coordinating the maintenance and procedures of several databases related to the namespaces and numerical spaces of the Internet, ensuring the network’s stable and secure operation. ICANN is the holder of all of the registered domains on the Internet and your domain provider has access to the ICANN database and registers your domain on your behalf. A small portion of your annual domain fees goes to support this organization.

Conclusion
If You Have Responded to a Phishing Email - Act Quickly!
Contact the institution that impersonated quickly and have them freeze, cancel, and re-issue credit cards. Change passwords on any accounts quickly and update the security settings on the account. Change the account user ID if you are able to do so. Update any other accounts that use the same user ID and password combination.
Phishing is a Criminal Act - Report it!
Phishing is a leading cause of identity theft. Education and changing email behaviors will go a long way toward reducing the risk of being victimized by criminals. One of the reasons why phishing is so prevalent is that conviction rates are extremely low and most cases go unreported by victims. We simply delete an email and move on with our lives.
Report instances of phishing or other cybercrime to the real business or organization that the scammers are pretending to be. Contact the scammed company or organization at an email address or phone number that YOU KNOW TO BE CORRECT. Most large companies take phishing very seriously and have the resources to investigate and work with law enforcement agencies to bring charges when possible.
The Federal Trade Commission has educational resources and a mechanism available for reporting phishing and other cybercrime. The Anti-Phishing Workgroup is an international coalition of counter-cybercrime responders, forensic investigators, law enforcement agencies, technology companies, financial services firms, university researchers, NGOs, and multilateral treaty organizations operating as non-profit organizations.
Federal Trade Commission
Anti-Phishing Working Group

DISCLAIMER:
The information presented above comes from personal and client experiences and is my opinion of best practices. I am not receiving compensation from any of the sites, products, or services that I mention in this posting. The examples presented have been altered to remove sensitive information not relevant to this article. I have no affiliation with the corporations or organizations referenced in this article other than as a customer of their services at times.
Resources
I’d like to thank the authors of the following blogs and websites. Their work provided some background research for this article.
- Phishing: Federal Trade Commission – https://www.ftc.gov/business-guidance/small-businesses/cybersecurity/phishing
- Report Fraud: Federal Trade Commission – https://www.ftc.gov/business-guidance/small-businesses/cybersecurity/phishing
- Anti-Phishing Workgroup – https://apwg.org
- Phishing: North Carolina Department of Justice – https://ncdoj.gov/internet-safety/phishing/
- ICANN Lookup – https://lookup.icann.org/en
- WHOIS Lookup – https://www.whois.com